Category Archives: Governance Audit

The Microbial Horizon: Calibrating Risk Management Timeframes for the Community Banks

The Perpetual Environment of Institutional Risk

In the physical world, a human body does not encounter biological threats on a scheduled, monthly basis. Microbes, bacteria, and viruses exist continuously in the environment—surrounding the body, resting on its surfaces, and operating within its internal pathways. They exist as a fundamental condition of biological life.
In the financial ecosystem, institutional risk operates under the exact same biological paradigm.

Risk is not a scheduled event; it is a permanent environmental entity that keeps evolving.

As long as a banking entity holds a sovereign charter, accepts a single dollar of local deposits, or executes a single digital transaction, risk exists alongside it, outside it, and deep within its core infrastructure.
Every Community Bank already possesses structured, legacy control systems. Without them, federal regulators would instantly revoke their banking license.
Yet, just because an institution possesses standard compliance plumbing does not mean the underlying threats pause between formal reviews.
The critical architectural question facing a Board of Directors is not whether risk exists today, but how frequently can an institution meaningfully measure, monitor, and neutralize these financial pathogens before they cause systemic degradation?

The Asset Size Axiom: Scaling the Time Dimension of Governance

In banking, there is a definitive, unyielding operational law:
As the asset size and structural complexity of a banking institution increase, the timeframe for risk assessment and risk management must decrease.
=====================================================
  RISK MANAGEMENT TIME-SCALE
=====================================================
[ G-SIBs] ---> Real-Time/ Hourly/ Daily (needs AI Automated Layers, with AI layers monitoring AI layers)
[ National Banks ] ---> Daily / Weekly (ML Driven Frameworks, and AI layer) 
[ Regional Banks ]  ---> Weekly / Monthly (RMAS Managed Framework, ML driven Frameworks)
[ Community Banks ]  ---> Monthly / Quarterly (RMAS Managed Framework, ML driven Frameworks )
====================================================

For Global Systemically Important Banks (G-SIBs) and multi-trillion-dollar money-center entities, managing risk on a manual human timeframe is an operational impossibility. At that tier, transaction velocity dictates that anti-money laundering (AML), liquidity drift, and perimeter cyber threats be evaluated on a daily, hourly, or sub-second basis. This is where advanced, enterprise-grade Artificial Intelligence enters the architecture. While the industry has still not perfected automated real-time compliance—even within the largest institutions—the ultimate destination of the banking sector is an automated, End-of-Day (EoD) neural audit of the entire balance sheet.

However, for a U.S. community bank — where the median asset size holds around $400M, rural institutions operate between $100M and $200M, and urban community hubs cap out near $1B —needing daily AI-driven risk management creates extreme operational friction and cost inefficiency.

For the community banking tier, the optimal balance between resource expenditure and absolute institutional defense is achieved through a precisely engineered, two-layer temporal framework: Monthly Execution and Quarterly Strategic Oversight.

The Trilateral Framework of the Risk Management Advisory Service (RMAS)

Our flagship Risk Management Advisory Service (RMAS) is explicitly built to address the environmental reality of risk for banks under $10 Billion in assets (U.S. Community Banks). Rather than relying on vague, open-ended consultations, RMAS structures continuous tracking across multiple frontiers using a highly rigorous system of diagnostic questionnaires and specialized checklists deployed across two distinct timeframes:


1. The Quarterly Layer: Navigating the Macro Direction

Deployed at the end of each fiscal quarter, our aggregated Quarterly Risk Governance Checklists serve as the board-level compass. This layer tracks long-term, structural vectors that impact the macro health and capital survival of the bank:
    • Regulatory Shielding: Monitoring the formal execution milestones of active MRA or MRIA remediation paths.
    • Financial & Balance Sheet ALM: Assessing unrealized losses in Available-for-Sale (AFS) portfolios and mapping contingent liquidity backup windows with the Federal Reserve Discount Window and FHLB.
    • Structural Asset Inventories: Auditing the centralized corporate registry to prevent unmapped, decentralized “Shadow AI” tools from breaching the bank’s operational perimeter.

The quarterly layer ensures the Board of Directors and the C-suite maintain absolute clarity over the bank’s broader risk velocity, protecting long-term customer trust and capital adequacy.


2. The Monthly Layer: Managing Short-Term Financial Risks / Pathogens 

Four weeks in banking is an eternity when facing modern operational threats. Our granular Monthly Risk Execution Checklists focus entirely on active, tactical groundwork—neutralizing short-term risk pathogens before they have the chance to crystallize into catastrophic quarterly failures:

    • Defensive Cybersecurity Inspections: Verifying that cryptographic Multi-Factor Authentication (MFA) is active across 100% of branch endpoints and remote gateways to block Ransomware and Business Email Compromise (BEC).
    • Staff Vigilance Architecture: Conducting interactive, small-group Zoom training cohorts (5 to 20 employees) to continuously insulate your human capital against evolving social engineering scripts.
    • Transactional & Underwriting Sanity: Monitoring the directional velocity of early-stage credit delinquencies (30–89 days past due) and validating that automated adverse action disclosures perfectly match fair lending expectations. Your bank may be doing this already. In such a case, an additional layer of risk management will be put in place to shield the bank from any material events related to fair lending compliance.


Meaningful Protection Without Operational Exhaustion

That’s the goal. By dividing your defensive posture into structured monthly sprints and overarching quarterly audits, RMAS delivers the ultimate corporate benefit: it provides a community bank with global, enterprise-grade risk visibility without paralyzing daily operations.

We acknowledge that microbes are in the air every minute of the day. We recognize that threats against your $400M asset base are being generated by adversaries and macroeconomic shifts every single morning. But by partnering with an elite, diligent, disciplined, external advisory advisory structure that continuously monitors banking risk variables through a fixed, disciplined cadence, your board can confidently pursue strong revenue and deposit growth — by focusing on your biggest strengths, which are the deep connections you have with local communities and local businesses.
You do not need to build a multi-million dollar internal AI lab to protect your institution. You simply need to implement a comprehensive risk management shield that monitors the environment, flags anomalies, and ensures that your bank remains completely out of the regulatory crosshairs.

Risk Management as a Service: Why Modern Banks Are Paid to Carry Sophisticated Risk

The Existential Pivot of the Banking Entity
For decades, traditional financial institution playbooks treated risk as an adversarial variable — a necessary evil to be minimized, hedged away, or avoided entirely through rigid credit policies and tight operational controls. In the legacy era, a bank’s stability was judged by the size of its defensive walls.
But in an era dictated by hyper-accelerated neural networks, fluid geopolitical cyber threats, and structural margin compression, that passive posture is an existential liability. The modern reality is stark: Banking is not a capital-allocation business. It is a sophisticated risk-absorption business.

Modern banks are not paid simply to store fiat currency or match lenders with borrowers; they are compensated by the market and by corporate enterprises to act as a Risk Management as a Service (RMaaS) platform.

In a highly volatile macroeconomic environment, institutional profitability belongs exclusively to organizations that treat the identification, tiering, and orchestration of sophisticated risk as their core, monetizable product.

Architecture of the Risk Monetization Engine

To convert risk from a balance-sheet vulnerability into a premium service, a bank must shift its structural view of operations.
When we analyze the institutions successfully scaling their net interest margins (NIM) and non-interest fee income today, they operate under a unified, three-tier risk monetization architecture:
===================================================
RISK MGMT ASSET ARCHITECTURE (MONETIZATION ENGINES)
===================================================
1. ADVANCED UNDERWRITING ENGINE -> Capture Alpha on Complex Risks
2. OPERATIONAL FABRIC LAYER -> Monetize Fractional Trust Infrastructure
3. REGULATORY ARCHITECTURE  -> Safeguard Sovereign Privileges
===================================================

1. Arbitraging Complexity: Moving Beyond Vanilla Assets
Standard, low-risk lending assets are increasingly commoditized by digital-first fintech platforms and capital-market alternatives. To protect yields against margin leakage, sophisticated institutions utilize advanced machine learning architectures to underwriting highly complex, non-linear risk segments.  By applying Explainable AI (XAI) frameworks — such as integrating SHAP (SHapley Additive exPlanations) diagnostic tools into commercial loan workflows— banks can safely evaluate complex SME credit profiles that legacy scorecards reject. The bank is compensated precisely because it has developed the mathematical governance required to accurately price and carry volatility that others cannot understand and quantify.

2. Monetizing the Trust Infrastructure

Sovereign banking infrastructure is built on absolute systemic trust. Corporate enterprises face severe counterparty risks, operational leakages, and cross-border settlement frictions daily. When a bank provides treasury management, automated liquidity forecasting, or real-time trade finance structures, it is operating as an outsourced risk buffer.

The corporate client willingly pays premium transaction and advisory fees because the bank absorbs the underlying operational, clearing, and execution risks into its institutional balance sheet.


3. Sovereign Compliance as a Competitive Moat
Banking functions inherently as an outsourced arm of sovereign economic governance. Navigating the dense labyrinth of federal oversight— including Federal Reserve SR Letter 11-7 / OCC Bulletin 2011-12, bank secrecy acts (BSA), and evolving anti-money laundering (AML) protocols—is an immense operational burden.
A bank that masters this compliance landscape converts regulatory friction into a powerful market defense. By offering bulletproof, auditable governance structures, the bank shields its corporate ecosystem from legal and systemic disruption, capturing premier enterprise relationships that require regulatory-grade sanctuary.

Bulletproofing the Downside

The Boardroom Mandate Operating as a Risk Management as a Service platform does not mean courting reckless exposure.

The line between sophisticated risk monetization and public institutional failure is drawn by the quality of a bank’s governance.

For the Board of Directors and the Chief Risk Officer (CRO), managing a sophisticated risk posture requires four non-negotiable operational guardrails:

    • Granular Asset Inventory Frameworks: Every algorithmic, technical, and credit model must be dynamically cataloged and categorized using a strict tiered risk inventory (from Tier 1 regulatory-sensitive models down to low-risk automation scripts) to prevent fragmented shadow-deployments.
    • Immutable Technical Guardrails: Implementation of automated Policy-as-Code controls at the API gateway layer to prevent data provenance failures and Personally Identifiable Information (PII) leakage. All model executions and data transactions must reside within Write-Once-Read-Many (WORM) cloud repositories to ensure audit-ready posture for federal bank examiners.
    • Human-in-the-Loop (HITL) Operational Controls: Establishing definitive automated execution ceilings. For example, allowing AI engines to independently price or clear automated small business lines up to a specific limit, while triggering mandatory human escalation and circuit breakers for high-value or structurally anomalous parameters.
    • Strong Cyber Defense Posture: Recognizing that state-sponsored adversarial actors run multi-year silent reconnaissance campaigns within core banking infrastructure. Boards must treat cyber defense not as an isolated IT cost center, but as the foundational shield protecting the bank’s ability to safely carry risk.


The New Boardroom Paradigm

The institutions that will dominate the coming decade will not be those that ran from risk, but those that engineered the most robust, compliant, and transparent machines for carrying it.

When a banking leadership team shifts its mindset from defensive damage control to active Risk Management as a Service, the entire corporate culture changes.  It eliminates revenue and margin leakage, elevates customer trust, and ensures that when the market experiences severe economic contractions, your institution stands firm as a sanctuary of stability.

True risk management does not stifle growth — it provides the shield that allows a bank to scale aggressively, confidently, and safely ahead of the competition.


Case Study: AI Governance Implementation in a Regional Bank -Executive Presentation

Case Study: AI Governance Implementation: Executive Presentation Outline

Please Note: This post shares the Executive Presentation of the AI Governance implemented as described in this case study.
Governance Frameworks for Enterprise AI: Regional Bank Case Study

Subject: First Lakes Financial Bancorp | $42B AUM, Chicago, IL  (Hypothetical)

Target Audience: Board of Directors, CEO, COO, CFO, Chief Risk Officer (CRO), Chief Information Officer (CIO), Regulatory Compliance Committee, Executive Steering Committee


Slide 1: Strategic Context & Regulatory Imperative

  • Core Message: Proactive AI governance converts regulatory friction into a sustainable market advantage over regional and fintech competitors.
  • Key Content:
    • Operational Landscape: First Lakes Financial Bancorp (~120 branches in IL, IN, WI) needed to scale credit underwriting and AML monitoring to compete with national money-center banks.
    • The Catalyst: Heightened federal examiner focus under OCC Bulletin 2011-12 / Federal Reserve SR Letter 11-7 alongside compliance requirements under ECOA and FCRA.
    • The Challenge: Pre-governance hurdles included shadow AI usage across regional units, data lineage risks with PII, and regulatory pushback on black-box credit models.

Slide 2: The Enterprise AI Governance Framework

  • Core Message: Aligning technical controls with established SR 11-7 and NIST AI RMF frameworks establishes a clear, audit-ready operational model.
  • Key Content:
    • Organizational Structure: Established an Executive AI Steering & Model Governance Council co-chaired by the CRO and CIO.
    • 4-Tier Risk Classification:
      • Tier 1 (High Risk): Commercial/Consumer Credit Underwriting, Automated AML/BSA Monitoring, Fair Lending.
      • Tier 2 (Moderate Risk): Commercial Client Advisory Assistant, Deposit Forecasting.
      • Tier 3/4 (Low Risk): Internal IT Helpdesk, Document Summarization.

Slide 3: Technical Execution & Safety Guardrails

  • Core Message: Embedding policy-as-code and explainability directly into MLOps pipelines ensures real-time regulatory compliance.
  • Key Content:
    • Explainable AI (XAI): Integrated SHAP value diagnostics and counterfactual algorithms to automatically generate required adverse action reason codes for loan rejections.
    • Policy-as-Code & Privacy: Enforced Open Policy Agent (OPA) rules at API gateways to block unauthorized PII transmission, paired with WORM cloud audit trails.
    • Human-in-the-Loop (HITL) Controls:
      • Auto-Approval Ceiling: Small business credit lines up to $250K (Model confidence >92%).
      • Mandatory Escalation: Credit decisions $250K–$2M or low confidence scores automatically routed to senior credit officers.

Slide 4: Quantifiable Business & Regulatory Outcomes

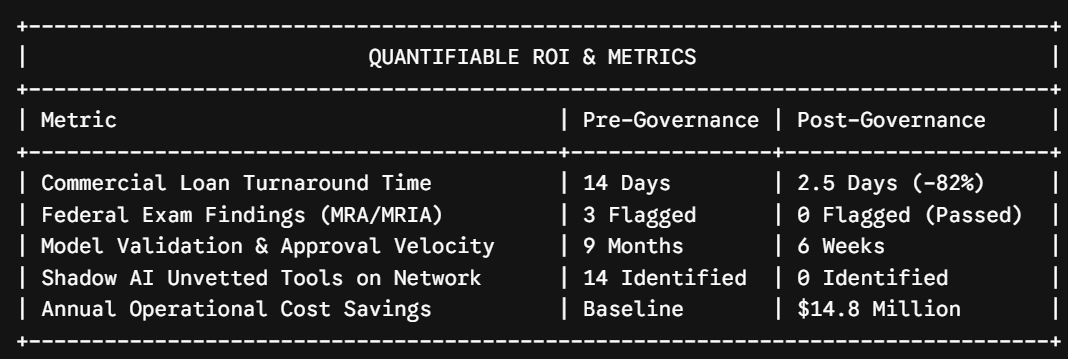
  • Core Message: Formal governance delivered a 100% compliant regulatory audit while dramatically improving operational velocity.
  • Key Content:
Metric Pre-Governance Post-Governance Impact / Improvement
Commercial Loan Turnaround 14 Days 2.5 Days 82% Acceleration
Federal Exam Findings (MRA/MRIA) 3 Flagged 0 Flagged Clean Regulatory Exam
Model Validation Velocity 9 Months 6 Weeks 83% Reduction in TTM
Shadow AI Tool Usage 14 Unvetted Tools 0 Unvetted Tools Complete Risk Mitigation
Annualized Operational Savings Baseline $14.8 Million Direct Bottom-Line Return

Slide 5: Strategic Lessons for a US Regional Bank

  • Core Message: Governance is an enabler of speed and trust, not a bottleneck to innovation.
  • Key Content:
    • Leverage Existing Standards: Building upon SR 11-7 and NIST AI RMF accelerates deployment cycles while maintaining regulatory alignment.
    • Prioritize Explainability Over Complexity: In regulated credit workflows, transparent, auditable models beat black-box architectures every time.
    • Clear Governance Accelerates Growth: Automated validation pipelines reduced model time-to-market from 9 months to 6 weeks, positioning First Lakes as a premier mid-market lender in the Midwest.

Governance Frameworks for Enterprise AI: Regional Bank Case Study

Note: This a composite case study, based on our observation and analysis of multiple regional banks. The names and numbers in this case study are hypothetical, and but the lessons are real.

  • Organization: First Lakes Financial Bancorp
  • Headquarters: Chicago, Illinois
  • Asset Size: $42 Billion AUM (Operating 120 branches across Illinois, Indiana, and Wisconsin)

Background & Operational Context

First Lakes Financial Bancorp, a regional bank headquartered in Chicago, built its reputation on commercial real estate lending, mid-market business banking, and personalized wealth management. Facing margin pressures from national tier-one banks and digital-first fintechs, executive leadership launched a strategic initiative to deploy enterprise-grade AI applications to streamline credit underwriting, automate regulatory anti-money laundering (AML) monitoring, and launch an AI-driven commercial client advisory assistant.

However, as a regional institution regulated by the Federal Reserve, the FDIC, and the OCC (Office of the Comptroller of the Currency), First Lakes faced strict regulatory scrutiny under US banking guidelines—specifically OCC Bulletin 2011-12 / Federal Reserve SR Letter 11-7 on Model Risk Management.

The Pre-Governance Challenge

Prior to adopting a formal AI governance framework, First Lakes experienced significant operational and regulatory friction:

  • Fragmented Shadow AI Deployments: Multiple commercial lending units independently adopted unvetted third-party credit scoring tools, creating unmapped algorithmic risks and data lineage gaps across regional offices.

  • Regulatory Pushback: During a periodic examination, federal regulators flagged an experimental machine-learning credit scoring model for lacking clear explainability, questioning whether the model complied with the Fair Credit Reporting Act (FCRA) and the Equal Credit Opportunity Act (ECOA).

  • Data Silos and PII Risks: Customer transaction data from legacy core banking databases was being manually exported by analytics teams to fine-tune open-source models, raising acute risks around Personally Identifiable Information (PII) leakage.

Implementation of the AI Governance Framework

To address these vulnerabilities, the Board of Directors established the Enterprise AI Steering & Model Governance Council, chaired by the Chief Risk Officer (CRO) and Chief Information Officer (CIO), with active participation from Legal, Information Security, and Commercial Banking heads.

First Lakes deployed a four-phase governance architecture tailored to US regional banking regulations over a 12-month period.

==========================================
FIRST LAKES BANK AI GOVERNANCE ARCHITECTURE
==========================================
1. STRATEGIC RISK TIERING (SR 26, SR 11-7, and ECOA Alignment)
2. EXPLAINABLE MLOPS (SHAP & Counterfactuals)
3. DATA & OPA (WORM Logging & PII)
4. HUMAN-IN-THE-LOOP CHECKPOINTS (Automated Escalation & Circuit Breakers)
==========================================

Phase 1: Strategic Risk Tiering & Model Inventory

Aligned with SR 11-7 guidelines and global risk frameworks (such as NIST AI RMF), First Lakes cataloged every analytical asset into a centralized model inventory and instituted a four-tier risk classification:

  • Tier 1 (High Risk / Regulatory Sensitive): Commercial & Consumer Credit Underwriting Models, Automated AML/BSA Transaction Monitoring, and AI-driven Fair Lending Assessments.

  • Tier 2 (Moderate Risk): Commercial Client Advisory Assistant, Liquidity & Deposit Forecasting Models.

  • Tier 3 (Low Risk): Internal IT Helpdesk Automation, Automated Document Summarization for Wealth Managers.

Phase 2: Explainable AI (XAI) for Fair Lending Compliance

To satisfy ECOA requirements, the bank mandated that no credit model could operate as a “black box.”

  • Engineering teams integrated SHAP (SHapley Additive exPlanations) and counterfactual reasoning algorithms into the credit evaluation engine.

  • For every adverse credit decision (e.g., loan denial or rate increase), the system automatically generated specific, rank-ordered Adverse Action Reason Codes (such as high debt-to-income ratio or insufficient liquidity history) required by federal lending laws.

Phase 3: Technical Guardrails & Data Provenance

  • Policy-as-Code Enforcement: Using Open Policy Agent (OPA) integrated at the API gateway layer, First Lakes blocked any unauthorized outbound API calls containing sensitive customer PII or account numbers.

  • WORM Audit Trails: All model inputs, retrieved context blocks from internal vector databases, and model outputs were immutably recorded in Write-Once-Read-Many (WORM) cloud repositories, creating an audit-ready log for federal bank examiners.

Phase 4: Human-in-the-Loop (HITL) Execution Rules

To balance speed with regulatory compliance, First Lakes established strict operational execution boundaries:

  • Automated Approval Ceiling: The credit AI was permitted to auto-approve small business credit lines up to $250K only if the model’s confidence score exceeded 92% and zero demographic variance anomalies were detected.

  • Mandatory Human Escalation: Any credit decision between $250K and $2M, or any applicant file triggering a confidence score below 92%, was automatically routed to a senior human credit officer alongside an explainability report.

Measurable Results & Regulatory Outcomes

By embedding formal governance directly into its technology stack and organizational culture, First Lakes Financial Bancorp achieved significant operational and business milestones within 12 months:

  • Clean Regulatory Audit: During the subsequent examination cycle, federal regulators commended First Lakes’ Model Risk Management framework as a best-practice implementation of SR 11-7 for artificial intelligence.

  • Operational Efficiency: Commercial loan decisioning speed increased by 82%, allowing the regional bank to effectively compete with national money-center banks for mid-market Chicago commercial accounts.

  • Demographic Fairness Verification: Quarterly algorithmic audits confirmed zero statistically significant disparity impact across loan applicants in primary markets (Chicago metro, Milwaukee, and Rockford).

Key Takeaways for US Regional Banks

  1. Leverage Existing Frameworks: US regional banks do not need to reinvent model management; mapping AI governance directly to existing SR 11-7 and NIST AI RMF standards satisfies regulators while accelerating safe adoption.

  2. Explainability Over Absolute Complexity: In credit and underwriting workflows, a slightly simpler, highly explainable model paired with SHAP diagnostic tools beats a complex black-box architecture that fails regulatory scrutiny.

  3. Governance Accelerates Velocity: Rather than delaying innovation, establishing clear risk tiers and automated CI/CD validation pipelines reduced First Lakes’ time-to-market for validated models from months to weeks.

Next: Please see the AI Governance Executive Presentation Outline.

Case Study: AI Governance Implementation in a Regional Bank -Executive Presentation

Tier 1 AI Risk Assessment Checklist for US Regional Banks

Tailored for evaluating High-Risk (Tier 1) artificial intelligence assets—specifically Credit Underwriting and Anti-Money Laundering (AML) / Bank Secrecy Act (BSA) transaction monitoring models—in accordance with Federal Reserve SR 11-7 / OCC Bulletin 2011-12 guidelines and the NIST AI Risk Management Framework.

1. Governance & Regulatory Alignment

  • [ ] SR 11-7 Model Inventory Registration: Ensure the candidate model is formally cataloged in the Enterprise Model Inventory with an assigned Model Owner, Risk Rating (Tier 1), and scheduled validation cadence.

  • [ ] Regulatory Scope Verification: Confirm model alignment with relevant federal mandates:

    • Credit Models: Equal Credit Opportunity Act (ECOA / Regulation B), Fair Credit Reporting Act (FCRA), and Fair Lending laws.

    • AML/BSA Models: FinCEN regulatory thresholds, USA PATRIOT Act compliance, and Suspicious Activity Report (SAR) filing triggers.

  • [ ] Model Governance Council Sign-off: Secure formal pre-deployment review approval from the Joint Model Risk Management (MRM) and AI Ethics Steering Committee.

2. Data Integrity, Privacy & Lineage

  • [ ] Data Provenance & Lineage Mapping: Document the full lifecycle of training, validation, and production data streams, identifying all source databases and transformation pipelines.

  • [ ] PII & Protected Class Sanitization:

    • Verify that prohibited variables (e.g., race, gender, age, marital status, national origin) are excluded from credit training datasets.

    • Implement automated scanning at API gateways to prevent raw PII leakage to third-party endpoints or unauthorized vector stores.

  • [ ] Data Quality & Representativeness Audit: Evaluate training data for historical bias, missing values, sample selection bias, and geographical representation across regional operating territories.

3. Conceptual Soundness & Model Architecture

  • [ ] Theory & Methodology Documentation: Document the underlying algorithmic methodology (e.g., Gradient Boosted Trees, Neural Networks, Logistic Regression) and justify why the chosen approach is suitable for the business objective.

  • [ ] Explainability (XAI) Architecture:

    • Credit Models: Implement SHAP (SHapley Additive exPlanations) or Integrated Gradients to ensure every credit decision can generate rank-ordered Adverse Action Reason Codes required by ECOA.

    • AML Models: Ensure transaction anomaly flags map to interpretable behavioral metrics (e.g., sudden velocity changes, structured cash deposits) for SAR documentation.

  • [ ] Hyperparameter & Optimization Audit: Validate that model hyperparameter tuning routines were logged and audited to prevent overfitting on historical training data.

4. Model Validation, Testing & Bias Diagnostics

  • [ ] Out-of-Sample & Out-of-Time Testing: Conduct rigorous backtesting using historical data across varying economic cycles (e.g., rate fluctuation periods or regional credit stress).

  • [ ] Fair Lending & Disparate Impact Analysis:

    • Perform statistical tests (e.g., Marginal Effect Analysis, Adverse Impact Ratios) across protected demographic groups to confirm compliance with 80% rule thresholds.

    • Test alternative less discriminatory algorithms (LESS/ADA) if baseline models demonstrate statistically significant demographic variance.

  • [ ] AML Sensitivity & False Positive Testing: Benchmark AML model detection rates against baseline rules engine performance, auditing false-positive reduction ratios and false-negative leakages.

  • [ ] Robustness & Adversarial Stress Testing: Conduct sensitivity testing against corrupted, synthetic, or adversarial data inputs to measure model stability under unexpected data drift.

5. Operational Deployment & Human-in-the-Loop (HITL) Controls

  • [ ] Policy-as-Code & Boundary Enforcement: Program dynamic business rules into execution gateways (e.g., setting hard credit line caps or minimum credit score thresholds independent of model output).

  • [ ] Human Escalation Thresholds:

    • Credit Underwriting: Define clear dollar thresholds (e.g., automated execution restricted to loans $\le \$250,000$ with $\ge 92\%$ confidence score; mandatory human underwriter review for all higher exposure or lower confidence cases).

    • AML Monitoring: Require mandatory BSA Officer review before closing any system-flagged suspicious transaction alert.

  • [ ] Circuit Breakers & Rollback Triggers: Implement automated kill-switches to halt automated execution if real-time error rates, drift thresholds, or system latencies breach predefined limits.

6. Continuous Monitoring & Audit Readiness

  • [ ] Data & Conceptual Drift Tracking: Deploy real-time telemetry to continuously monitor Population Stability Index (PSI) and Characteristic Stability Index (CSI) for input features.

  • [ ] Immutable Audit Logging (WORM Storage): Record all model queries, feature inputs, confidence scores, and outputs in Write-Once-Read-Many storage environments to ensure full auditability during federal regulatory examinations.

  • [ ] Periodic Re-Validation Schedule: Establish an automated trigger for comprehensive annual re-validation or emergency re-validation upon significant economic shocks or regulatory updates.

Model Validation Report (SR 11-7 / OCC 2011-12)

Model Validation Report
(SR 11-7 / OCC 2011-12)

Model Name: Commercial & Consumer Automated AI Credit Underwriting System (CAICUS)
Model Owner: Commercial & Consumer Credit Risk Division
Validator / Reviewer: Model Risk Management (MRM) Independent Validation Team
Model Risk Tier: Tier 1 (High Risk / Regulatory Sensitive)
Validation Date: September 2026

1. Executive Summary & Validation Verdict

1.1 Scope of Review

The Independent Model Risk Management (MRM) group conducted a full initial validation of the Commercial & Consumer Automated AI Credit Underwriting System (CAICUS) v2.4. This evaluation assesses compliance with Federal Reserve SR 11-7 / OCC Bulletin 2011-12, Equal Credit Opportunity Act (ECOA / Regulation B), Fair Credit Reporting Act (FCRA), and NIST AI RMF standards.

1.2 Overall Validation Rating

  • Verdict: Approved with Conditions
  • Risk Level: Tier 1 (High)
  • Re-validation Frequency: Annual (Next Scheduled: Q3 2027)

1.3 Key Findings & Mandatory Remediation Items (MRA/MRIA)

  • MRIA 2026-01 (High): Explainability Baseline: SHAP value calculations for commercial real estate exposure lack automated integration with legacy core system Adverse Action code generators. Remediation Due: 60 Days.
  • MRA 2026-02 (Medium): Data Stability Tracking: Population Stability Index (PSI) alert thresholds are set manually rather than dynamically updating across changing interest rate regimes. Remediation Due: 90 Days.

2. Model Overview & Business Context

Component Description
Business Purpose Automated underwriting, risk-based pricing, and credit line determination for small-to-mid enterprise (SME) and consumer loan applicants up to $250,000.
Model Architecture Gradient Boosted Decision Trees (XGBoost) combined with dynamic SHAP (SHapley Additive exPlanations) explainability layers.
Key Inputs Bureau credit scores, debt-to-income (DTI) ratios, liquidity history, 24-month transaction velocity, and verified business revenue.
Key Outputs Approved/Denied recommendation, recommended credit ceiling, risk tier score (1–10), and top 4 adverse factors (if denied).

3. Data Integrity, Lineage & Governance Audit

3.1 Data Lineage & Sanitization

  • Data Sources: Core banking transactional database, credit bureau API feeds, audited financial statements.
  • Prohibited Variables Verification: Confirmed total exclusion of protected class attributes (race, gender, age, marital status, national origin) and direct proxies in both training and operational feature stores.
  • Privacy Controls: Evaluated Open Policy Agent (OPA) integration at the API gateway layer to ensure customer PII is masked prior to model feature extraction.

3.2 Data Quality & Representativeness

  • Evaluated dataset completeness across primary operating territories (Midwest US regional foot-print).
  • Verified that historical loan performance data spans both expansionary and contractionary credit cycles (2018–2025 data range).

4. Conceptual Soundness & Algorithmic Design

4.1 Theoretical Justification

  • The selection of XGBoost over traditional logistic regression is justified by a 14% improvement in Gini coefficient performance on non-linear commercial relationship datasets.
  • Hyperparameter tuning frameworks were audited to ensure grid searches were constrained against overfitting on edge-case regional data.

4.2 Explainability (XAI) & Fair Lending Architecture

  • ECOA Reason Code Generation: The model utilizes global and local SHAP value rankings to extract the top four negative feature contributions for every adverse credit decision.
  • Audit Findings: Explainability pipelines operate accurately for consumer lending features, but require minor feature-mapping alignment for specialized commercial real estate metrics (refer to MRIA 2026-01).

5. Model Performance, Backtesting & Bias Diagnostics

5.1 Discriminative Power & Calibration

  • Receiver Operating Characteristic (ROC-AUC): 0.865 (Target >= 0.80)
  • Kolmogorov-Smirnov (KS) Statistic: 54.2% (Target >=45%)
  • Brier Score (Calibration): 0.042 (Demonstrates strong alignment between predicted default probability and observed defaults).

5.2 Disparate Impact & Fair Lending Testing

MRM conducted independent demographic fairness tests across protected classes using synthetic proxy matching and Bayesian Improved Surname Geocoding (BISG):
Metric Target / Benchmark Observed Result Status
Adverse Impact Ratio (AIR) >= 0.80
(80% Rule)
0.92 Pass
Marginal Effect Variance < 0.05 across cohorts 0.02 Pass
Standardized Difference in Means < 0.25 0.08 Pass

6. Operational Controls, HITL & Monitoring

6.1 Human-in-the-Loop (HITL) Rules

  • Auto-Execution Limit: Restricted strictly to credit applications <= $250K where model confidence >= 92%
  • Mandatory Officer Routing: Applications between $250K and $2M, or applications triggering confidence scores < 92%, are automatically routed to senior credit underwriters alongside the SHAP diagnostic payload.

6.2 Monitoring & Fallback Safeguards

  • Drift Telemetry: Real-time monitoring of PSI (Population Stability Index) and CSI (Characteristic Stability Index) configured with alerts at PSI> 0.10 (warning) and PSI > 0.25 (mandatory model halt).
  • Audit Trail Verification: Confirmed all inputs, feature vectors, SHAP outputs, and execution decisions are logged to WORM (Write-Once-Read-Many) compliant cloud infrastructure for regulatory inspection.

7. Sign-off & Approval Matrix

Role Name / Title Signature Date
Lead Validator VP, Model Risk Management [Signed] Sept 14, 2026
Head of MRM SVP, Enterprise Model Governance [Signed] Sept 16, 2026
Chief Risk Officer Executive VP, Chief Risk Officer [Signed] Sept 18, 2026